Configuration and administration
Connect WeCom
Configure WeCom login and member import.
Guide · Module: integrations · Developers · Deployment: Not specified · Confirmed product versions: Not specified · Source: Existing documentation
After connecting, enterprise members can log in to AskTable through an organization-specific link. AskTable imports only members within the custom application's visibility scope.
Prerequisites
- You are an Owner or Admin of the current AskTable organization;
- You can sign in to the WeCom administration console and create a custom application;
- Members' browsers can reach the AskTable login URL. Private deployments should use an HTTPS URL allowed by the enterprise platform and accessible from members' browsers.
Screenshots illustrate field locations; enterprise platform interfaces may change, so follow the actual console.
1. Create a custom application
In the WeCom administration console, open Application management → Custom → Create application, then enter an application name, introduction, and icon.
After creation, complete two settings on the application details page:
- Select the departments and members allowed to log in to AskTable in Visibility scope;
- Keep the application enabled and assign at least one application owner.
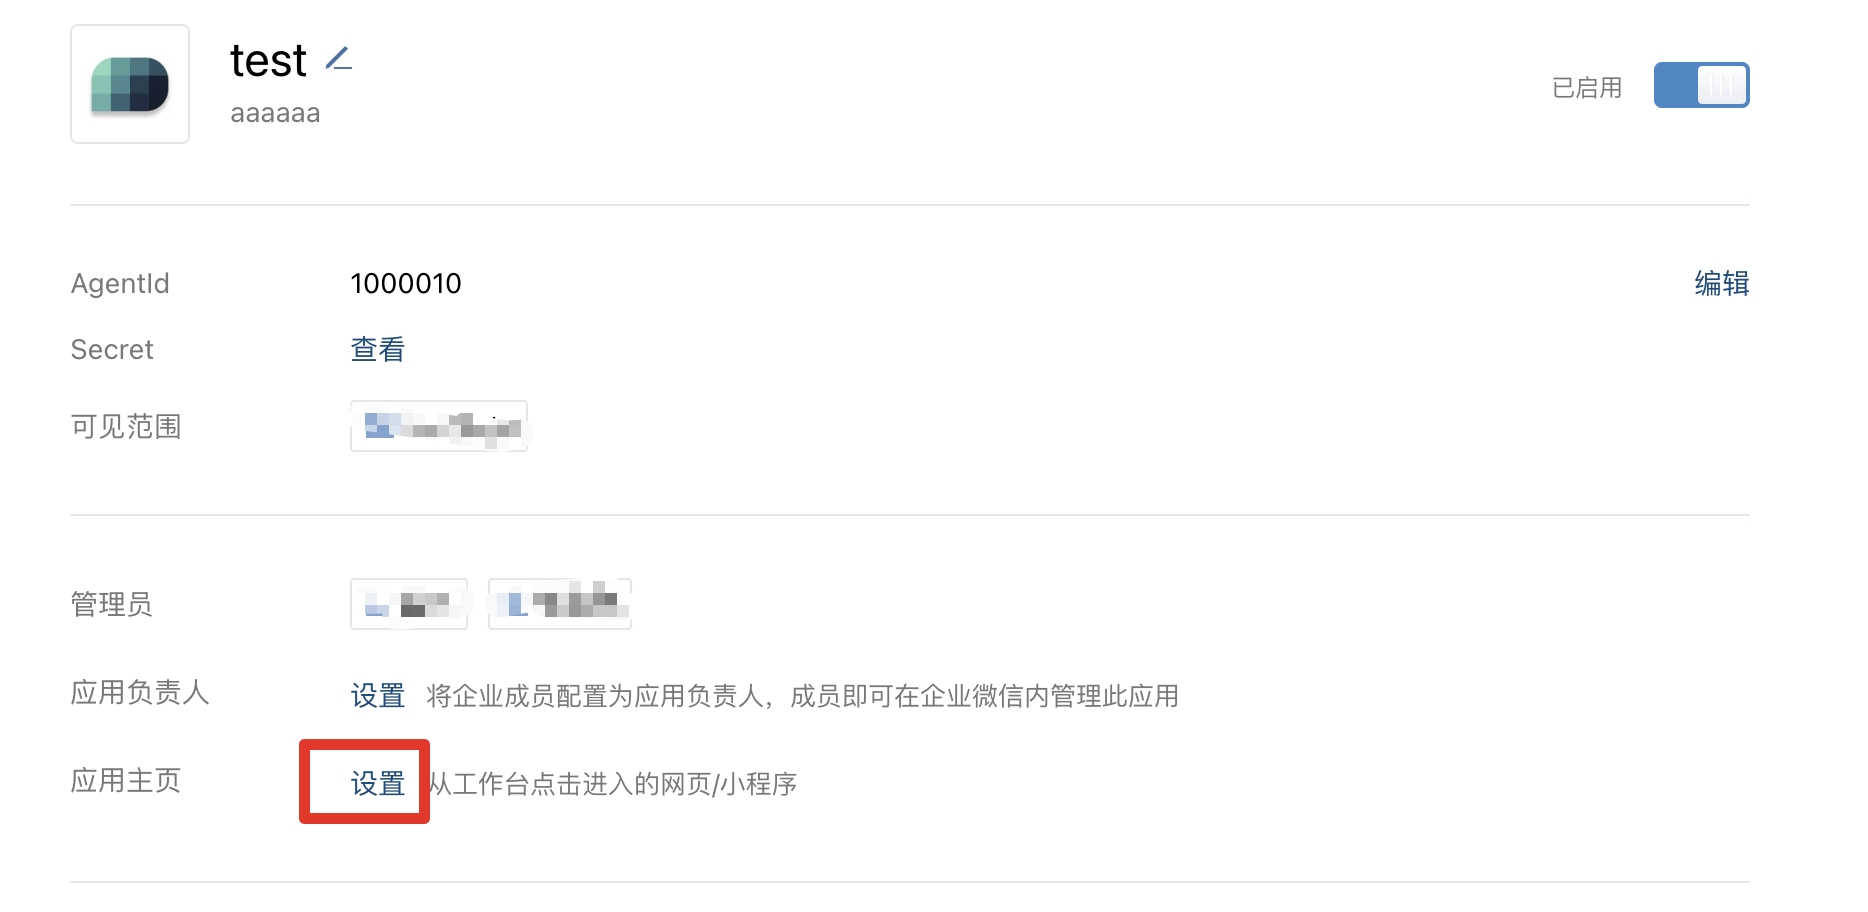
AskTable uses this visibility scope when fetching import candidates. Too narrow a scope makes target members unselectable; a wider scope shows more candidates but does not import them automatically.
2. Obtain three credentials
Prepare the following information:
| AskTable field | Location in WeCom |
|---|---|
| CorpID | My enterprise → Enterprise information → Enterprise ID |
| AgentID | AgentId on the custom application details page |
| Secret | Secret → View on the custom application details page |
Secret is a sensitive credential and should be stored only in AskTable configuration. If you reset Secret in WeCom, update it in AskTable too.
3. Enable the integration in AskTable
Open Profile → Organization → Enterprise integrations → WeCom, read the introduction, and click Enable. Enter CorpID, AgentID, and Secret in the dialog, then click Enable.
Enabling only saves configuration; it does not immediately verify credentials or import members automatically. URL, import, and editing actions below become available only after saving succeeds.
4. Configure the application homepage and authorization domain
After enabling, copy Callback URL from Login URL in AskTable. Return to the WeCom custom application details page, click Application homepage → Set, select Webpage, and enter the complete callback URL in Webpage URL.
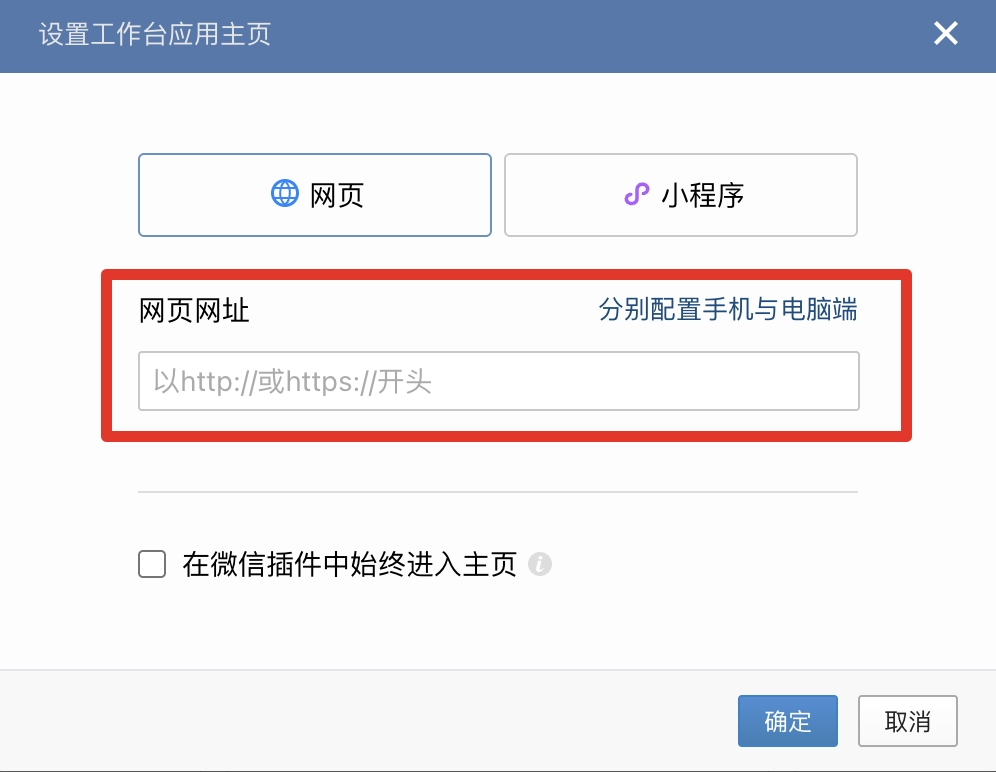
If the WeCom console requires a trusted domain or authorization callback domain under Web authorization and JS-SDK, use the domain from the AskTable callback URL without protocol or path. For example, if the callback URL is https://example.com/login/sso/wecom, enter example.com. Cloud URLs also include ?org_id=..., but domain entry works the same way.
5. Select members to import
Return to AskTable and click Import members. Search, filter, and select people in the dialog. The page shows remaining slots; after successful submission, it shows newly added and existing member counts.
- New members join the organization as Members;
- Existing members' roles do not change;
- Removing upstream members does not automatically disable AskTable members;
- Synchronization does not automatically restore disabled AskTable members.
To adjust candidate scope, first change Visibility scope on the WeCom custom application, then reopen the import dialog.
6. Verify login
- Confirm the test member is within application visibility and has been imported successfully;
- Open the custom application from the WeCom workspace, or open the AskTable callback URL in the member's browser;
- Complete WeCom authorization and confirm the correct AskTable organization opens.
First-time enterprise login does not create members automatically. The test member must already be imported, with both AskTable user and organization membership active.
Troubleshooting
Candidate lookup or import fails
- Check that CorpID and Secret come from the same enterprise;
- Confirm Secret has not been reset;
- Check that the custom application's visibility scope includes the target department or member;
- Check whether WeCom restricts trusted IPs for API calls; if so, add the AskTable deployment's outbound IP.
Cannot authorize after opening the application homepage
- Confirm the application homepage uses the full callback URL copied from AskTable;
- Confirm the trusted domain matches the callback URL's domain;
- Confirm the application is enabled and the test member is visible to it;
- Local must use the parameter-free URL shown on the page; Cloud's
org_idcannot be removed or changed.
Change enterprises
CorpID cannot be edited directly after enabling. Disconnect the integration on the details page first, then enable it again with the new enterprise's credentials. Disconnecting does not delete existing users, organization members, or project data.
For more identity scope and disconnection rules, see Enterprise integration login.
After importing, assign project roles and data access scope; see Invite members and Set data access scope.